AI Found PHP’s Hidden Flaw, but the Patch Race Showed How Little Time Defenders Have
AI Found PHP’s Hidden Flaw, but the Patch Race Showed How Little Time Defenders Have
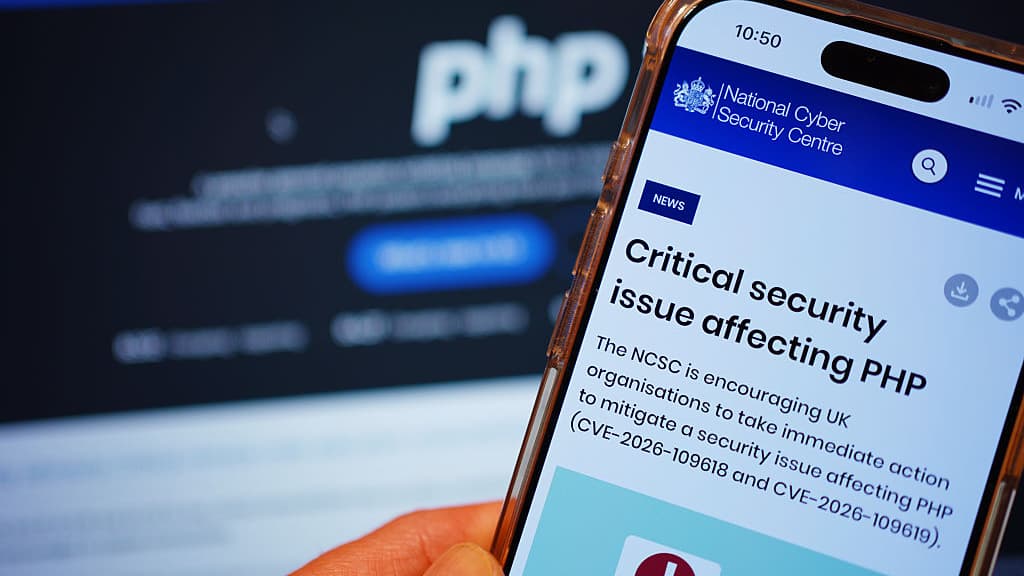
The crisis began in August, when separate research teams at Wiz and Calif, working with advanced AI models, uncovered related flaws buried in PHP’s core code for more than a decade. The bugs could give an outsider command-level control of an unpatched web server—a serious prospect for a language estimated to underpin about 70% of the web.
For the researchers, this was proof that AI can strengthen the defensive side. Wiz researcher Sagi Tzadik said agents can compress “months of traditional research” into days or even hours, though humans still had to spend days understanding and reproducing the bug. The PHP maintainers, rival security firms and other specialists then spent weeks working toward a patch under coordinated disclosure.
That orderly process fractured this week. Details began circulating before the planned release, and the PHP Foundation said Chainguard had “unilaterally broke the embargo,” disrupting weeks of coordination. Chainguard CEO Dan Lorenc said he acted because he believed exploitation was already under way; others disputed that assessment. The result was the nightmare defenders had hoped to avoid: public clues, incomplete fixes and a rapidly expanding target list.
Cloudflare recorded thousands of attempted exploits before the announcement, then tens of thousands within 45 minutes, hundreds of thousands within two hours and eventually millions. Governments and companies from Europe to Asia pulled services offline while applying updates. For Dutch cyber chief Matthijs van Amelsfort, the immediate prescription was brutally simple: “patch, patch, and patch.”
Officials stressed that attempts are not confirmed breaches, and ordinary visitors do not need to patch their phones merely for browsing a PHP site. The urgent risk lies with website operators: an unpatched server could expose data, be altered or become a launchpad for attacks elsewhere.
The response is already being productized. Aravind Srinivas said Computer credits were being offered to check sites for PHP exposure, an example of AI being turned toward the cleanup as well as the discovery. Yet the deeper warning remains: OpenAI expects similar findings to rise sharply, while PHP patcher Ondřej Surý called this a “disaster waiting to happen” for a long time.
Write a comment